When conducting field research among vulnerable populations—whether evaluating refugee assistance programs, tracking maternal health interventions, or surveying financial access, data security is far more than an IT checkbox. It is an ethical obligation and a core programmatic requirement.
Yet, many research teams and non-profits continue to collect Personally Identifiable Information (PII) using standard commercial form builders or unencrypted cloud spreadsheets.
When sensitive survey responses are stored on unverified third-party servers, shared via unencrypted file exports, or accessed on unsecured mobile devices, your organization faces severe reputational, legal, and operational risks.
Here is why generic survey tools fall short on data protection, and how modern enterprise platforms secure the entire research lifecycle.
The Vulnerabilities of Standard Data Collection
Commercial survey tools are designed primarily for marketing feedback and customer satisfaction polls, where data sensitivity is low. When applied to social impact, health, or humanitarian studies, these generic tools introduce critical security gaps:
- Unencrypted Local Storage: If an enumerator tablet is lost, stolen, or confiscated in a high-risk field environment, unencrypted survey responses stored on the device can be easily extracted, exposing sensitive respondent identities.
- Lack of Granular Role-Based Access: Standard tools often provide all-or-nothing access permissions. Field supervisors, enumerators, data analysts, and external donors frequently share credentials or gain full view of raw PII that they do not need to see.
- Unregulated Data Residency and Sovereignty: International grantmakers and national data protection authorities enforce strict regulations on where personal data can be stored and processed. Generic cloud tools rarely give you control over data hosting locations or encryption keys.
Building a Zero-Trust Data Pipeline
To protect beneficiary privacy and comply with stringent international security standards, research organizations must adopt a zero-trust approach to field data management.
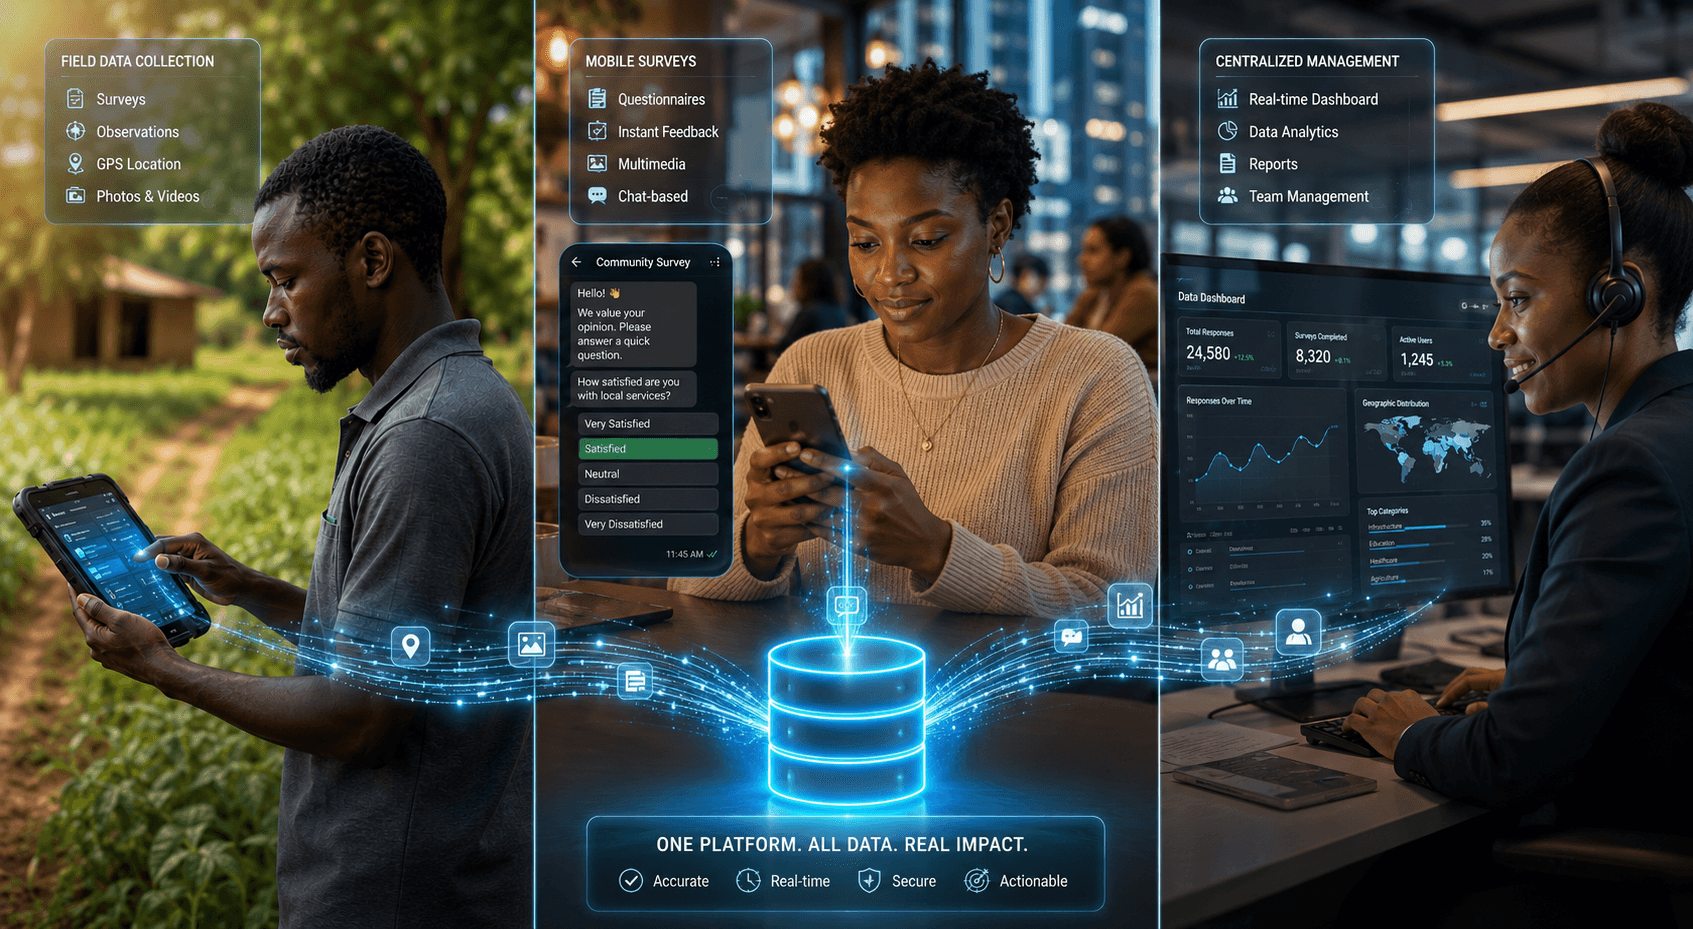
This is why security-conscious organizations rely on KAPsurvey to safeguard their field operations. Engineered from the ground up with enterprise-grade security, KAPsurvey ensures that sensitive data remains protected at rest, in transit, and during analysis.
Here is how advanced security architecture elevates field data protection:
- End-to-End Encryption at Rest and in Transit: Data collected on the KAPsurvey mobile app is encrypted locally on the device using AES-256 encryption. Even if a field tablet is physically compromised, stored data remains unreadable without cryptographic authentication.
- Automated PII Anonymization: Project directors can flag specific survey variables as PII—such as names, phone numbers, or national ID numbers. The platform automatically isolates or redacts these fields before raw data reaches analysts or public dashboards.
- Strict Role-Based Access Control (RBAC): Assign precise permissions across your entire operational team. Enumerators can only submit data for their assigned clusters, supervisors review specific geographic teams, and analysts work strictly with de-identified datasets.
Protect Your Respondents, Protect Your Mission
Trust is the foundation of effective field research. When respondents know their personal information is completely secure, they share far more accurate, honest, and reliable insights.
Don't let legacy security vulnerabilities compromise your organization's mission, beneficiary trust, or donor compliance.
Visit KAPsurvey today to learn how our secure, enterprise-grade research platform protects your data from the field tablet to the final report.